Raw prompt
Untrusted input arrives from a person, an app, or a browser chat. Cards, emails, identity numbers, and secrets are still in the clear.
Technologies
Infrastructure Appinico keeps, explained on its own. NoeticGuard is first. The list can grow.
AI security and data masking
Zero Leak architecture. Personal data is tokenized on the device before a prompt reaches OpenAI, Claude, Gemini, or your own model. Raw prompts stay local. NoeticGuard does not need them in order to mask.
noeticguard.com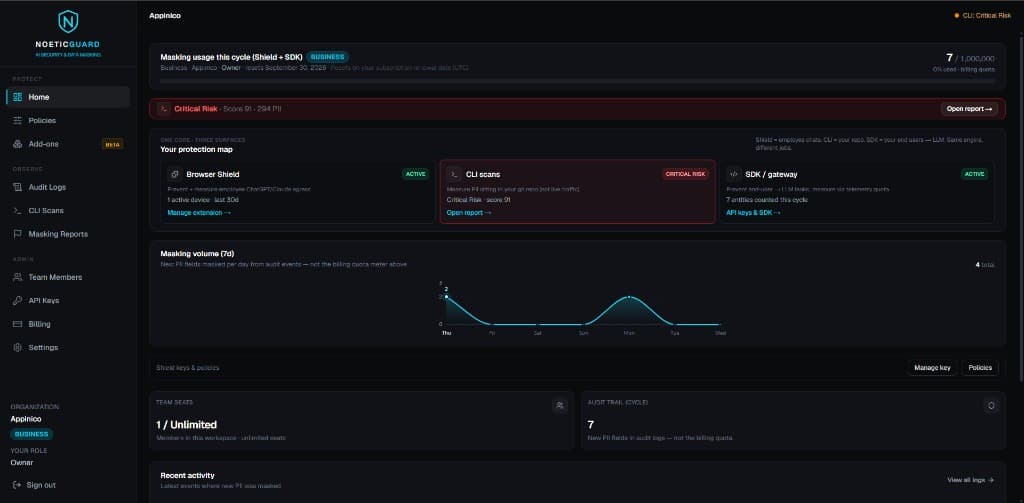
How a prompt moves
Untrusted input arrives from a person, an app, or a browser chat. Cards, emails, identity numbers, and secrets are still in the clear.
The core engine tokenizes that data into a local vault. The model receives placeholders such as [EMAIL_1] or [CREDIT_CARD_1], not the original values.
The LLM answers with those vault tokens. It never sees the raw personal data, so it cannot echo it back in the clear.
On the way back, vault values are restored only for the person who already had them. A blocked competitor name stays blocked. It is not reversible.
Same engine, three doors
Masks PII inside ChatGPT, Claude, and Gemini web chats on the device, before the prompt leaves the browser. Built for employee chats on a managed browser with Shield installed.
Scans a local repo for PII sitting in code and opens a masked risk report. Same engine as Shield. Useful before Copilot or another assistant reads the tree.
Mask user text in your backend, then call any LLM API. Policy and quota can sync. The raw prompt stays in your process. Industry packs add detectors. They are not a second product.
Shield, CLI, and SDK share the same on-device core. The live console is the place that engine is watched, not a separate cloud masking service.
Identical values reuse the same token in a session, so a repeated email stays [EMAIL_1]. Traces stay readable without sending originals to the model.
It sits between the prompt and the LLM, not inside Slack, Gmail, or endpoint DLP. Only masked, vault-safe payloads are meant to cross that boundary.
Local-first masking is oriented to GDPR and CCPA-style privacy programs, with detectors for common PII such as emails, cards, and national ID formats used across major markets. Those labels are orientation aids. They are not certifications, audits, or attestations.
Zero Leak assumes a managed browser with Shield installed. Incognito and unmanaged Chrome need a device policy. The SDK may call home for license and policy bundles only. Raw prompts and payloads stay on your machines.